
Every Microsoft 365 migration has a surprise waiting in it.
A Power Automate flow owned by someone who left two years ago. A SAML certificate that expires the week after cutover. A mailbox on litigation hold that nobody told you about. A private channel with 40 GB in it that isn’t in your SharePoint numbers.
You don’t find these in the admin centres. You find them on go-live weekend.
A full tenant assessment used to take me half a day of clicking through admin centres, exporting CSVs and stitching them together in Excel. So I built a script to do it for me. V9.10 is the biggest update yet, and it’s built to find those surprises first.
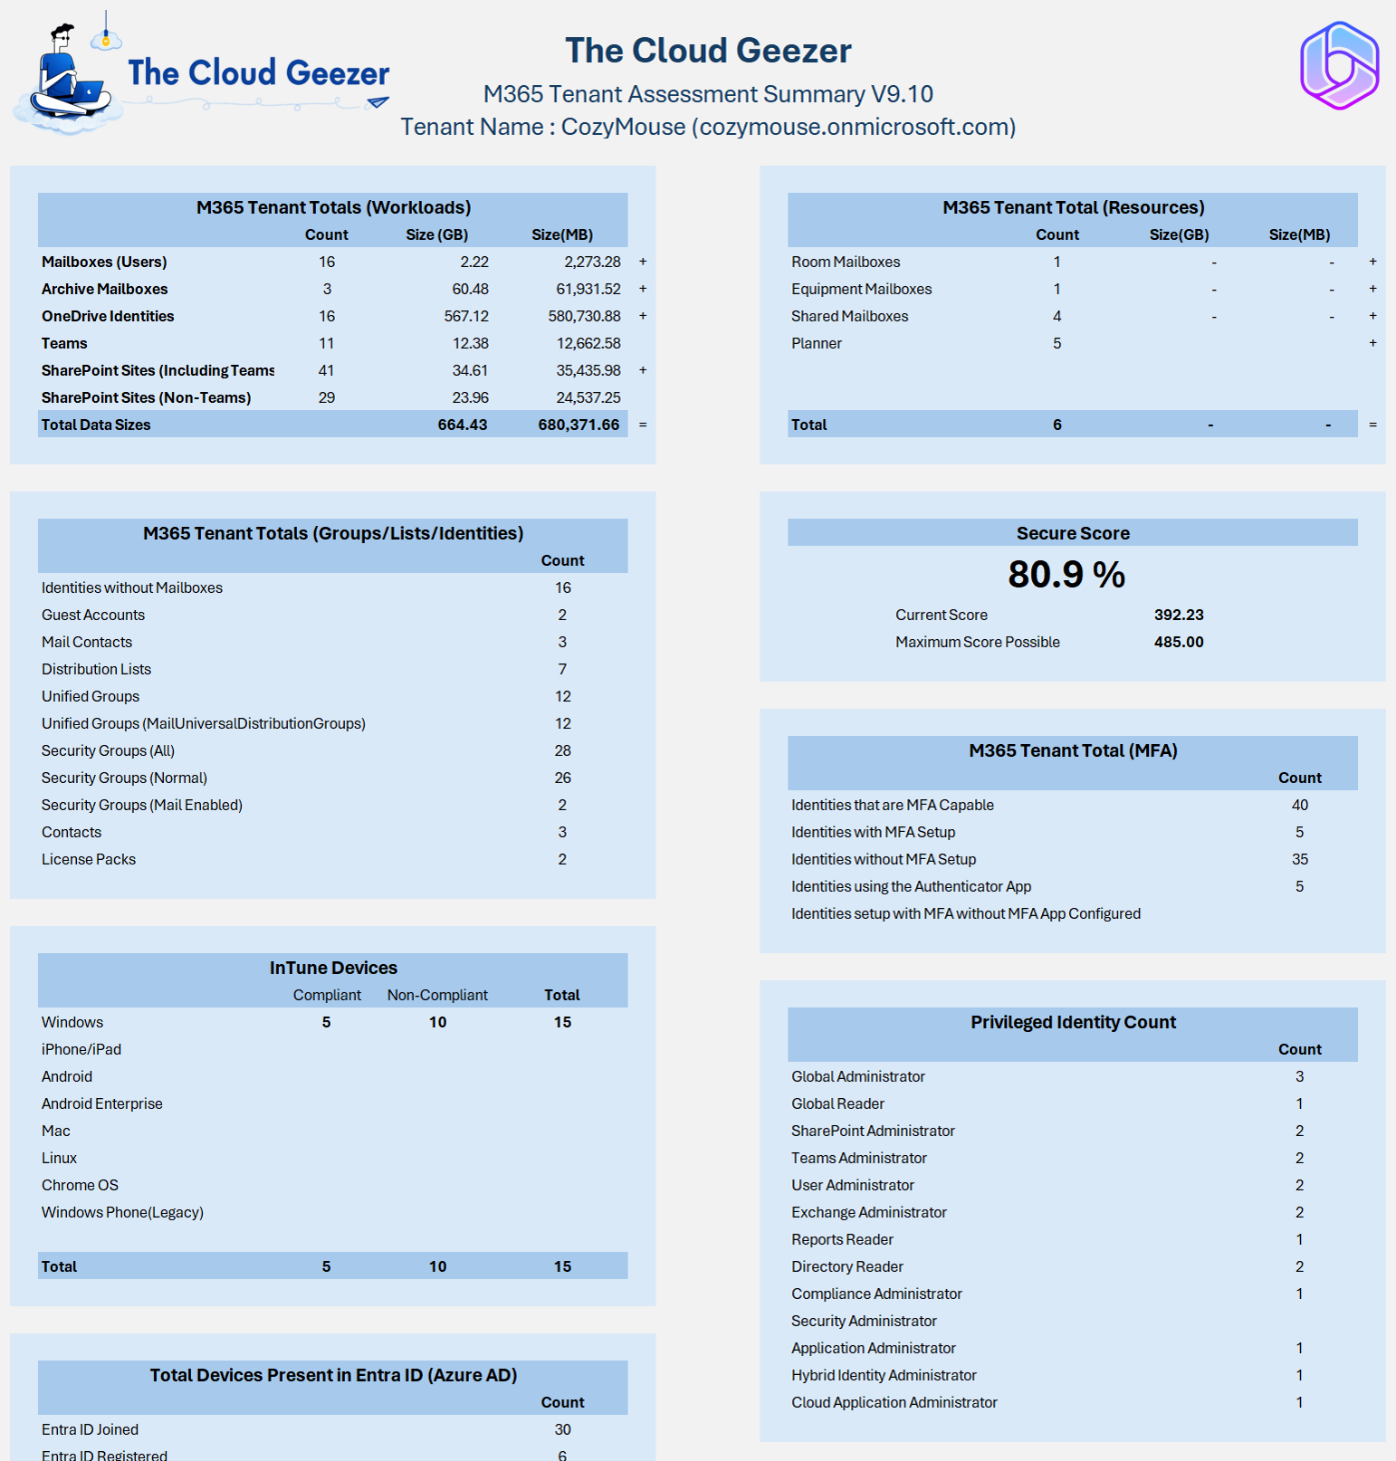
One PowerShell run. One Excel workbook. More than 60 sheets. A summary page that sizes the whole tenant at a glance.
https://store.thecloudgeezer.com/products/microsoft-365-discovery-script
What’s New in V9.10 (October 2026)
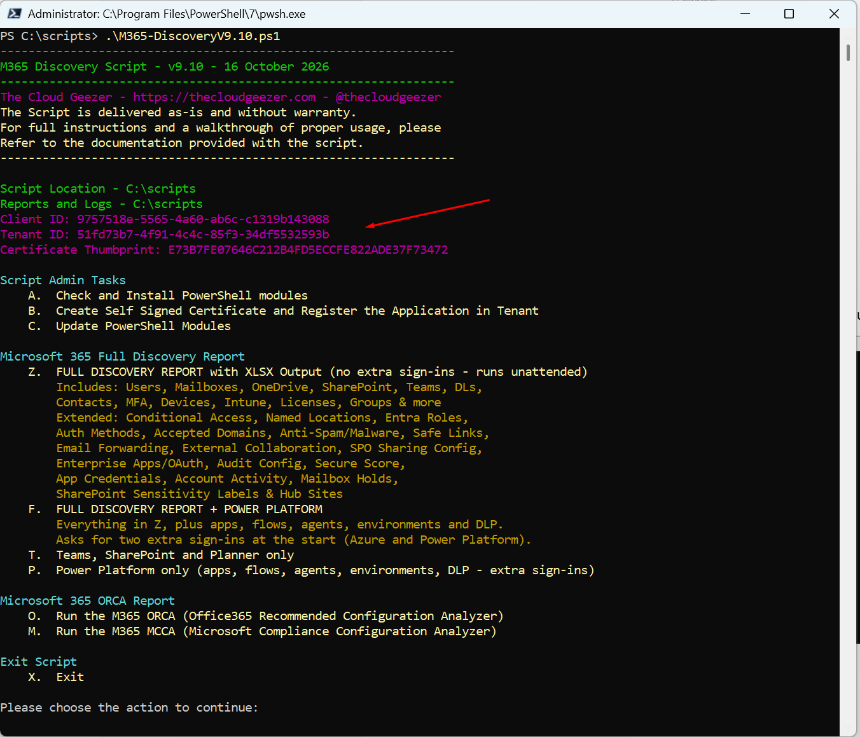
- ⚡ Power Platform: every app, flow and Copilot Studio agent, with each owner checked in Entra ID. Orphaned apps and disabled owners are flagged. It also reports environments, DLP policies and tenant settings.
- 🔑 App secrets and certificates: every client secret and certificate on app registrations and enterprise apps, including SAML signing certificates. Each one is marked expired, expiring within 30 days or expiring within 90 days.
- 👤 Account activity: inactive accounts, accounts that have never signed in, disabled users still holding a licence, and directory sync health for hybrid tenants.
- ⚖️ Mailbox holds: litigation, retention, eDiscovery and delay holds, plus organization-wide holds, with a migration note on every affected mailbox.
- 🏷️ SharePoint sensitivity labels and hub sites: the label and hub for every site, and accurate library sizes.
- 📁 JSON and CSV output: every run gets its own folder, and you can rebuild the report later without reconnecting to the tenant.
- 📋 Run Log: a sheet that tells you exactly what was collected, what was skipped and why. If one section can’t be read, the rest of the report still completes.
Everything Else It Covers
It still covers everything you need to scope a migration:
- 📧 Mailboxes: user, shared, room and equipment mailboxes with sizes, item counts and archives, plus Full Access and Send As permissions and forwarding rules
- ☁️ OneDrive and SharePoint: every site, subsite and library with true sizes, file counts, templates and sharing settings
- 💬 Teams: standard, private and shared channels, channel storage, owners and members, plus Planner plans
- 👥 Groups: Microsoft 365 groups, security groups and distribution lists, all with members
- 🔐 Identity: MFA methods per user, Conditional Access policies shown by name, admin role assignments, password expiry and guest accounts
- 💻 Devices: Entra ID devices with BitLocker status, and Intune devices, compliance policies, config profiles and apps
- 🛡️ Exchange security: anti-spam, anti-malware, Safe Links, Safe Attachments, connectors, transport rules and audit settings
- 📊 Licensing and apps: Secure Score per control, enterprise app permissions by name, and licence usage
Built for Migration Planning
The Excel output is designed to be used as a migration runsheet. Every sheet can be filtered, and the key sheets include a Migrate column, so you can batch and group users, mailboxes, sites and Teams straight from the report. The summary tab gives you the headline numbers for any scoping conversation: mailbox, archive, OneDrive, Teams and SharePoint storage, along with groups, MFA, devices, privileged roles, Secure Score and all the new V9.10 checks.
The MFA sheet shows, for every user, whether MFA is set up and which methods they use: Authenticator app, phone, FIDO2 key, Windows Hello, email, software token or Temporary Access Pass.
It’s far more practical for planning than the standard Microsoft 365 admin centre reports, because everything sits in one place and lines up.
Lifetime Updates
Buy once and every future update is yours. Whenever a new version is released, everyone who has bought the tool gets a new download link. If you already own V8.12, your V9.10 update is on its way.
Required Modules
The script checks for and installs what it needs from the menu (option A):
- Microsoft.Graph.Authentication: the only part of the Microsoft Graph SDK it needs now. All Graph calls are made directly, so the full Graph module is no longer required.
- ExchangeOnlineManagement: for the Exchange Online sections
- ImportExcel: for the Excel output
- Az.Accounts and the Power Platform admin module: only needed if you run the optional Power Platform section
Everything is read-only. The tool never changes anything in your tenant.
Administrative Rights Required
- To register the app (one time only): a Global Administrator. The script creates the app registration and certificate for you and opens the consent page.
- For the main discovery run: nothing extra. The script signs in with its own app and certificate, so the standard run has no sign-in prompts and runs unattended.
- For the optional Power Platform section: sign in with a Power Platform Administrator, Global Administrator, Dynamics 365 Administrator or Global Reader account when prompted.
The script creates the application registration, assigns its read-only permissions and updates the config file for you.
Upgrading from V8.12? Delete the existing app registration in Entra ID and run option B again, so the new read-only permissions are added.
ORCA / MCCA Report
In the update in December 2023, the tool includes the ability to run the Microsoft ORCA report from inside the script. The ORCA Report is the Office 365 Recommended Configuration Analyzer and gives solid information and recommendations for the tenant with regard to mail/inbound/outbound security. An example is here.
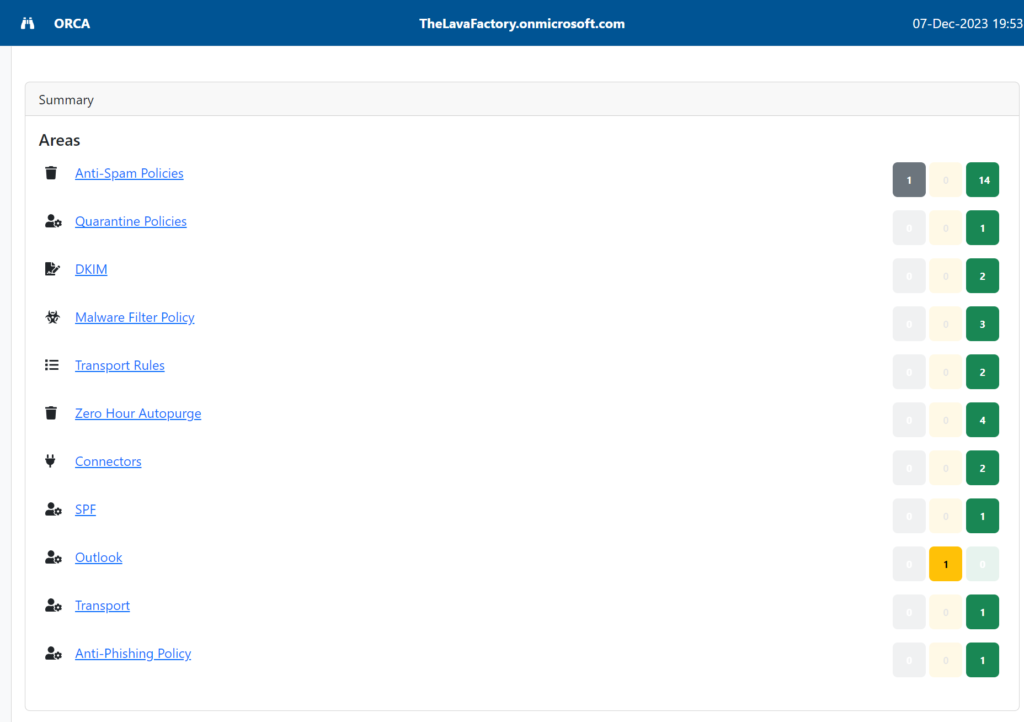
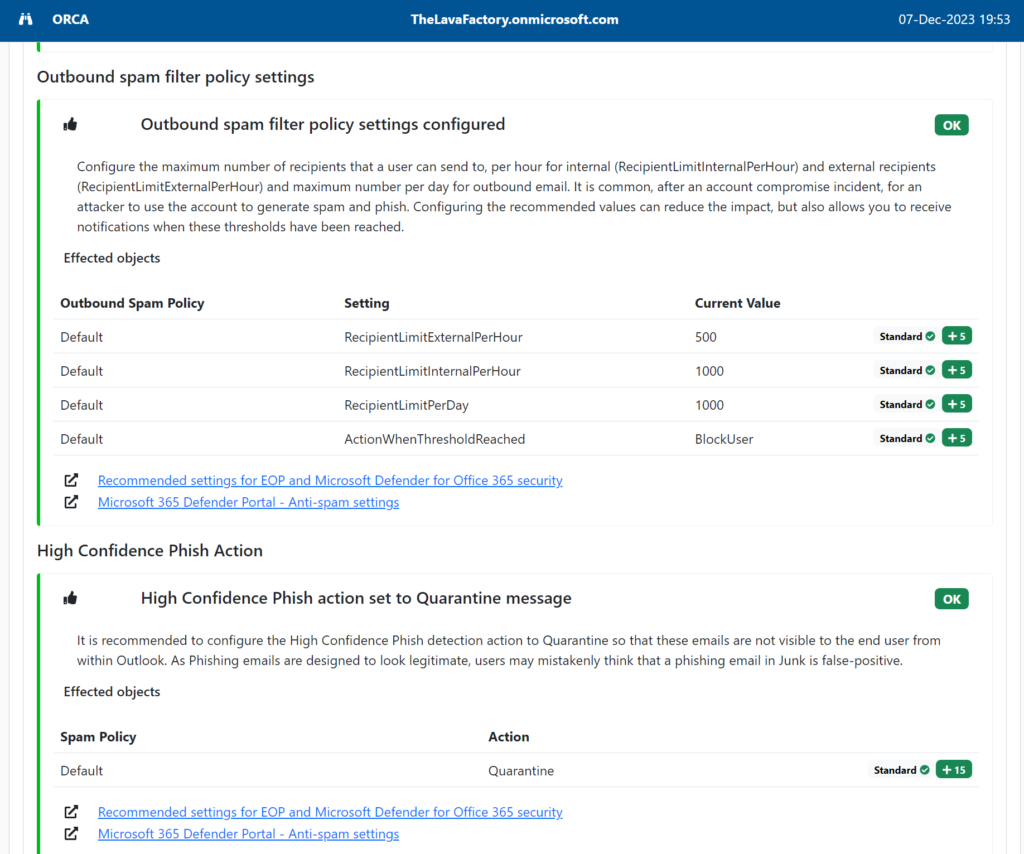
An extremely useful report when looking at your own, or a clients, tenant. Likewise, the MCCA report was also added and can be triggered from the main menu. This gives a great couple of additional reports that are always interesting and well received by the client that you are running this for on their tenant.
https://store.thecloudgeezer.com/products/microsoft-365-discovery-script
The Menu and Output
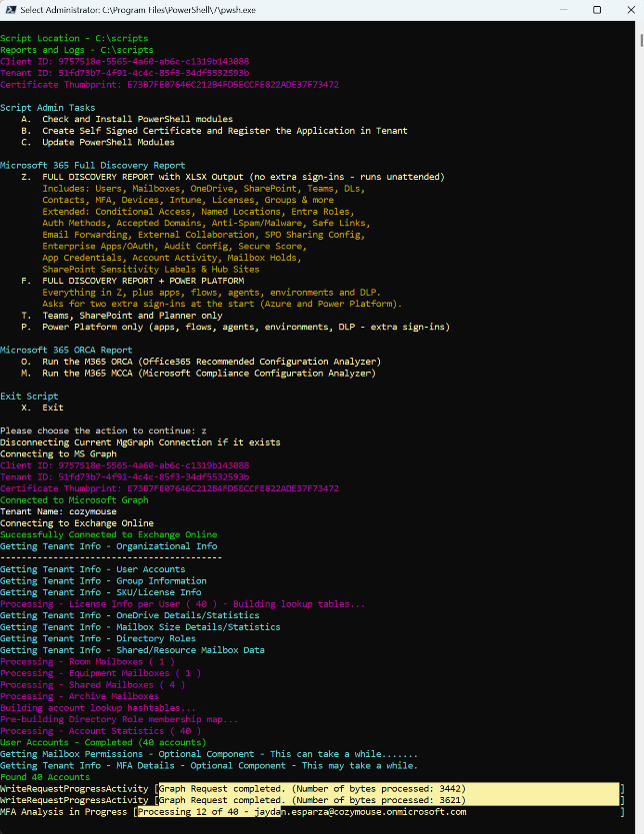
The menu now gives you a choice of how much to collect:
O / M – ORCA and MCCA reports
Z – Full discovery: everything, unattended, with no sign-in prompts
F – Full discovery plus Power Platform: asks for two extra sign-ins at the start, then runs unattended
T – Teams, SharePoint and Planner only
P – Power Platform only
Each run creates its own folder containing the Excel workbook, a JSON copy of all the data and one CSV per sheet.
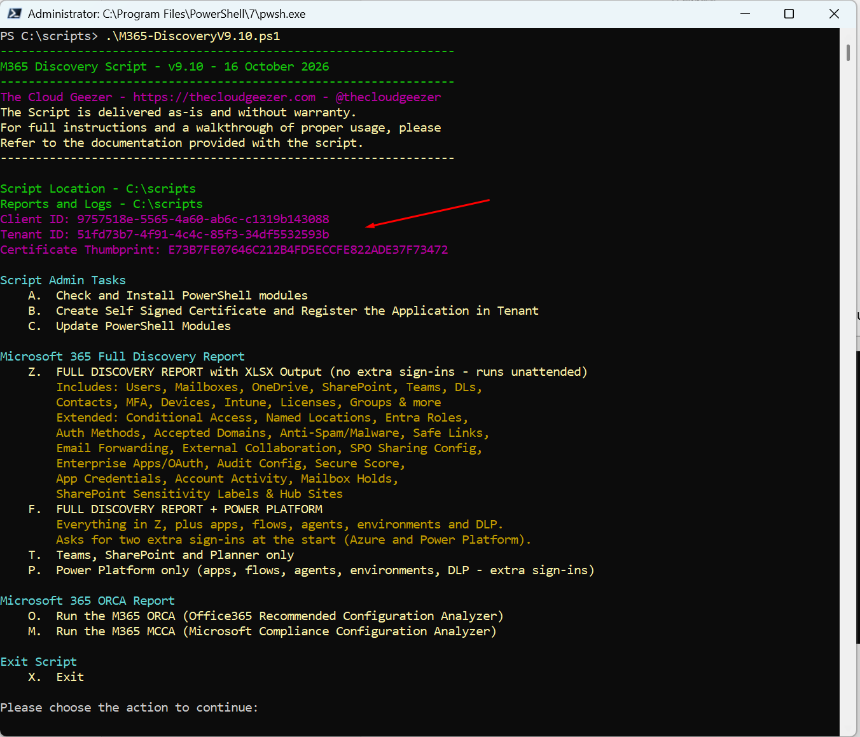
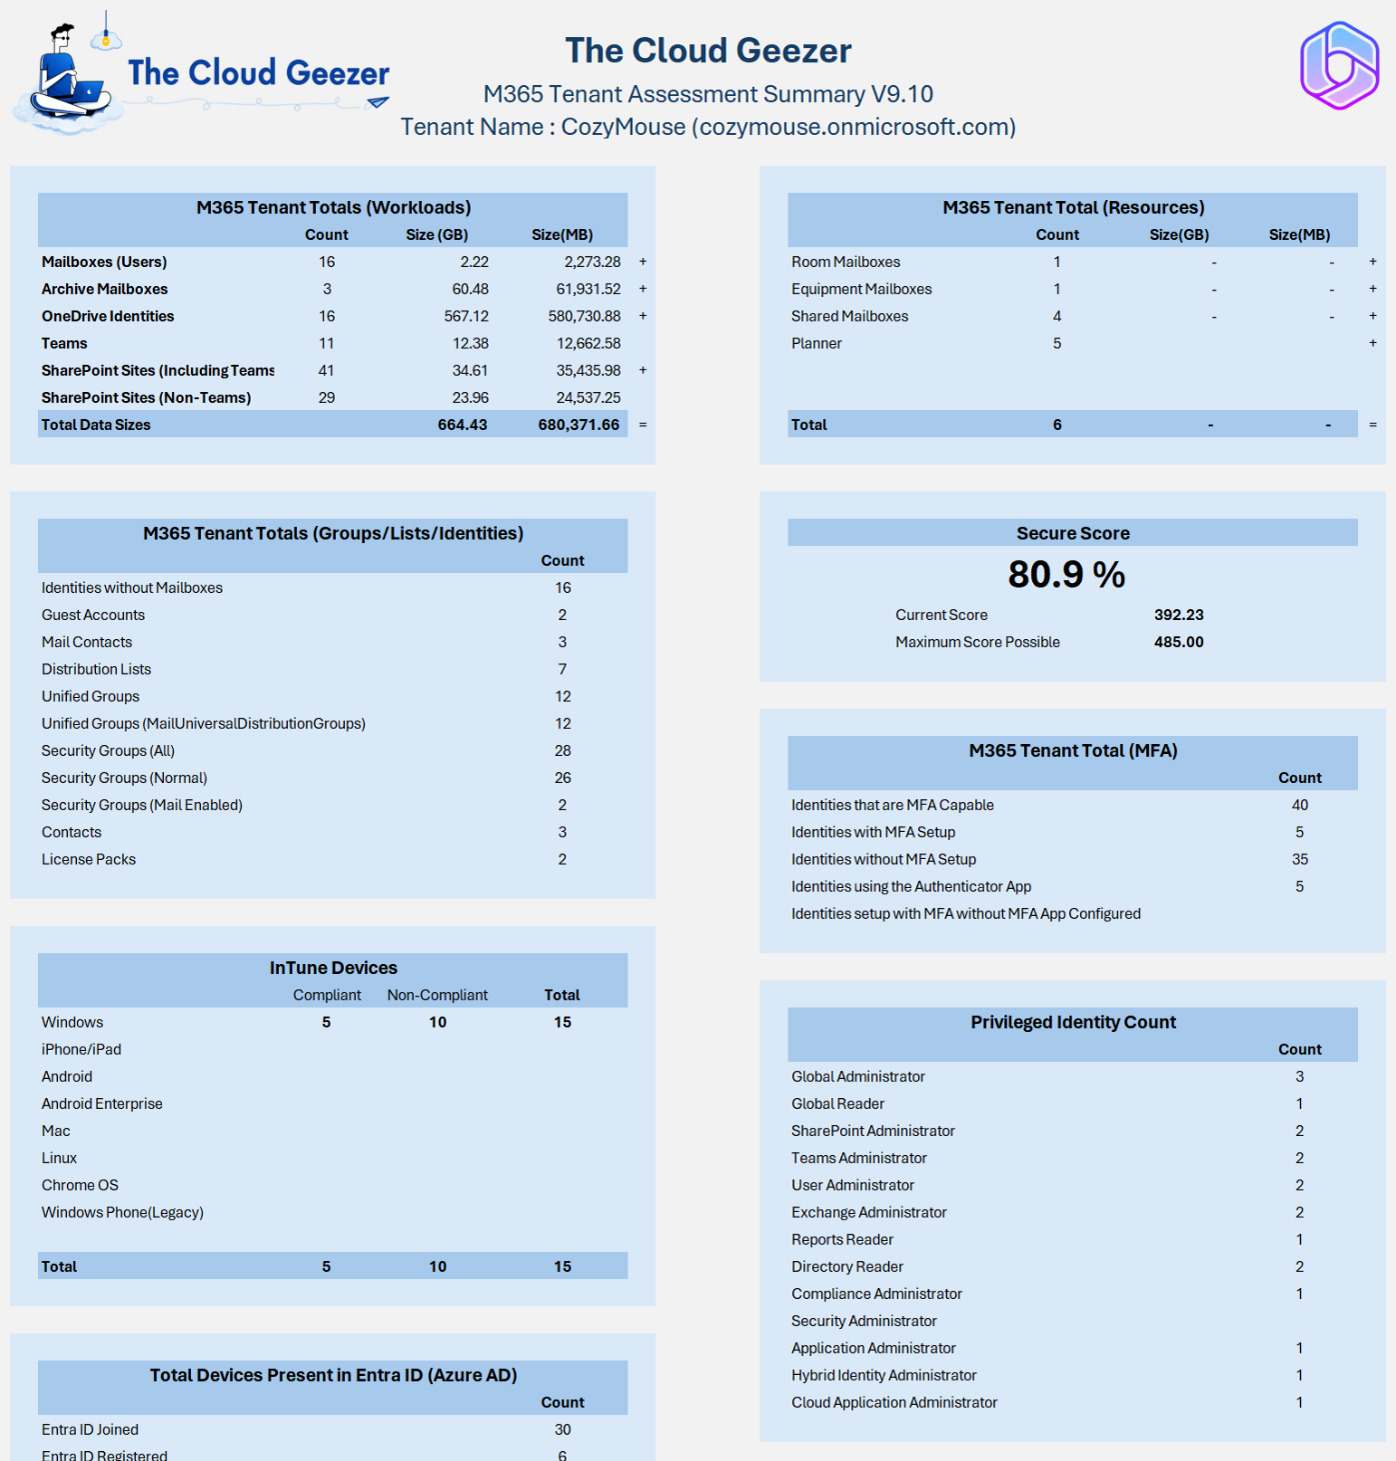
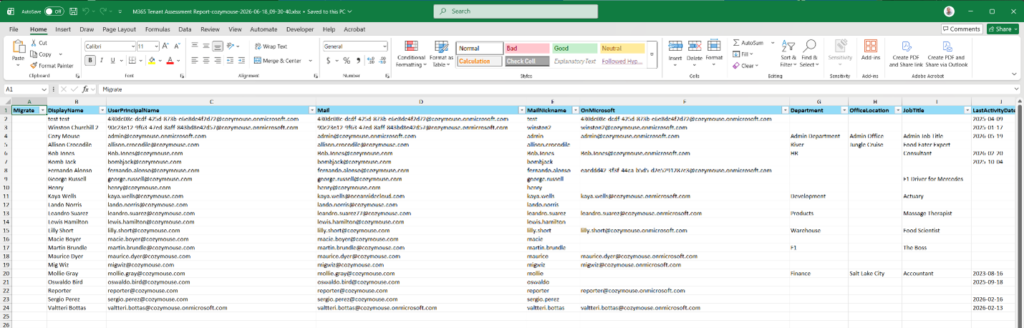
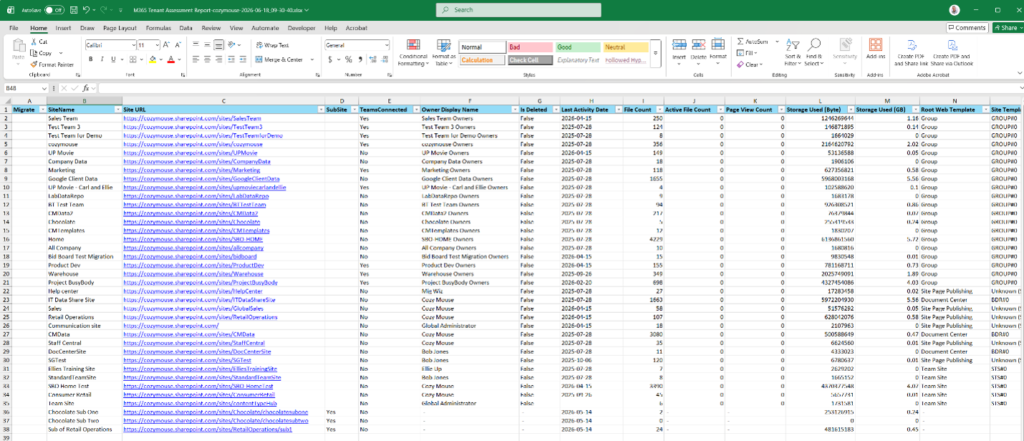
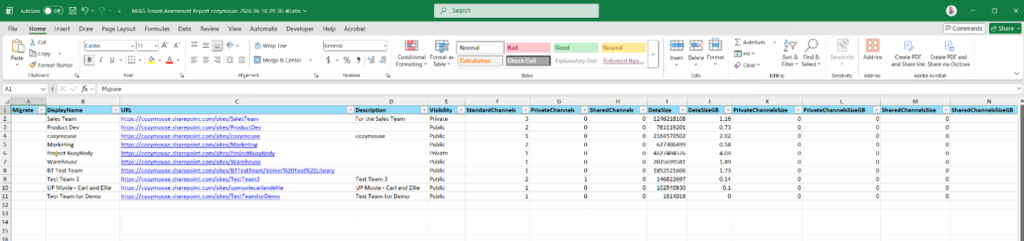
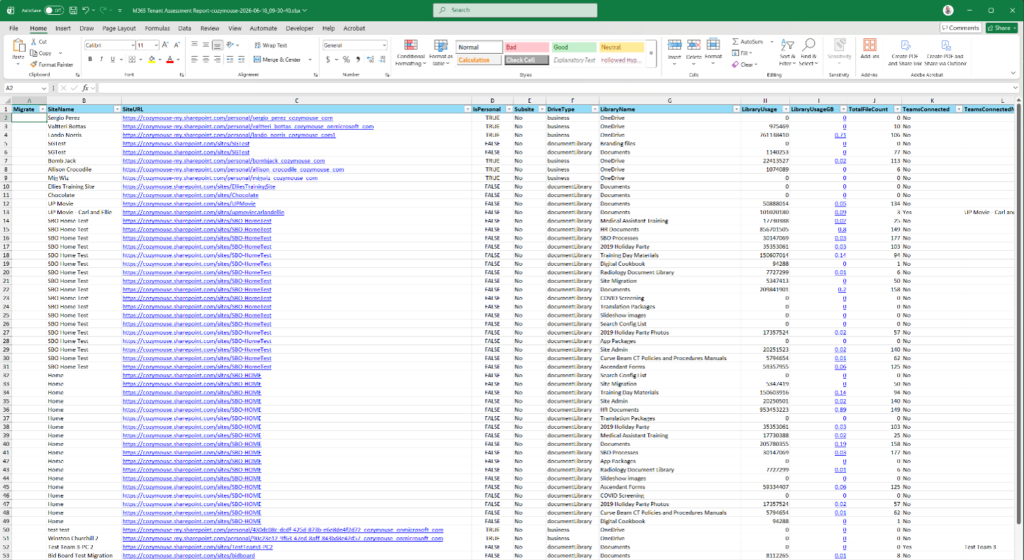
Everything is run from a simple menu to make it easy to get the output you need.
https://store.thecloudgeezer.com
Downloading and Running
- The download is a ZIP containing the launcher script, the tool module, the summary template, the config file, a full step-by-step guide and the changelog.
- Extract it to any folder you like.
C:\scriptsis no longer required. Keep all the files together in that folder. - If Windows blocks the downloaded files, run
Unblock-Fileon them (the guide has the exact command). - Open a new PowerShell window, run the launcher, and use option A to install the modules, option B to register the app, then option Z or F.
- Reports go into the script folder by default, or anywhere you choose with
-OutputPath.
In Summary
What’s the worst thing you’ve found mid-migration that discovery should have caught? Let me know in the comments, along with any ideas for what you’d like to see in the next version. You can also email me at mark@thecloudgeezer.com.
Hope you find this useful, please reach out in the comments with any thoughts, comments or improvements you would like to see.
Mark – The Cloud Geezer – mark@thecloudgeezer.com
